Email confidentiality, clearly explained
Is your email really confidential?
A secure connection protects an email while it moves. It does not, by itself, prevent the servers along the way from processing its content.
Follow the message
Every connection is encrypted.
At first glance, everything looks reassuring. Send the simulated email to see what TLS protects—and what it does not.
🔒 The connections are encrypted.👁 The relay can nevertheless process the message content.
TLS encryption protects the message while it travels between two machines. Each SMTP server must nevertheless process the message before establishing the next connection.
Confidentiality therefore depends not only on encryption. It also depends on who operates the intermediaries.
The email has reached its recipient.
In practice
A normal email. Secured in transit. Visible inside the relay.
The same message, followed from its TLS settings to the copy processed by the cloud SMTP relay.
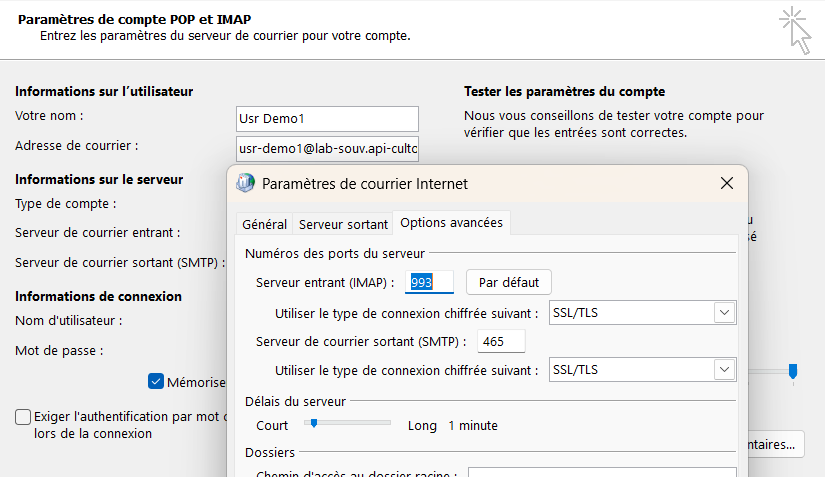
TLS is enabled
Incoming and outgoing connections both use SSL/TLS. The transport is encrypted before the message leaves the workstation.
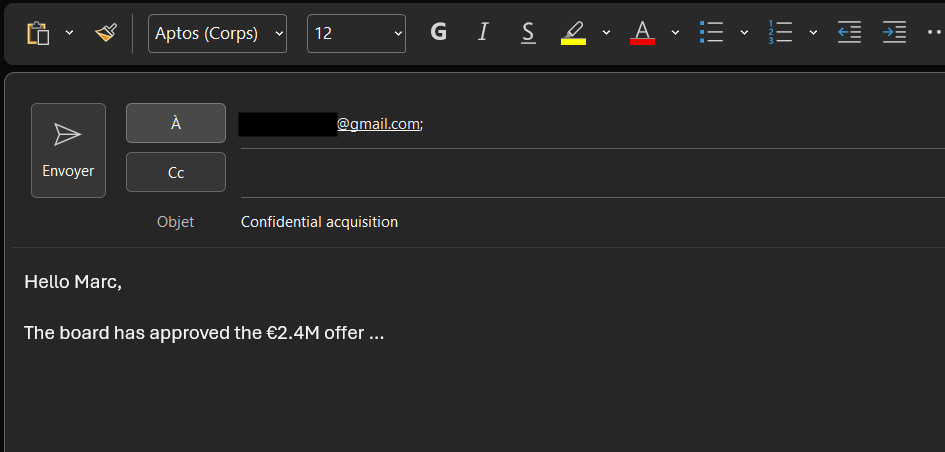
The message is written normally
No unusual workflow: the user writes and sends the email from a familiar desktop mail environment.
The relay processes the content
Inside the cloud SMTP relay, the sender, recipient, subject and message body are available to the service handling delivery.
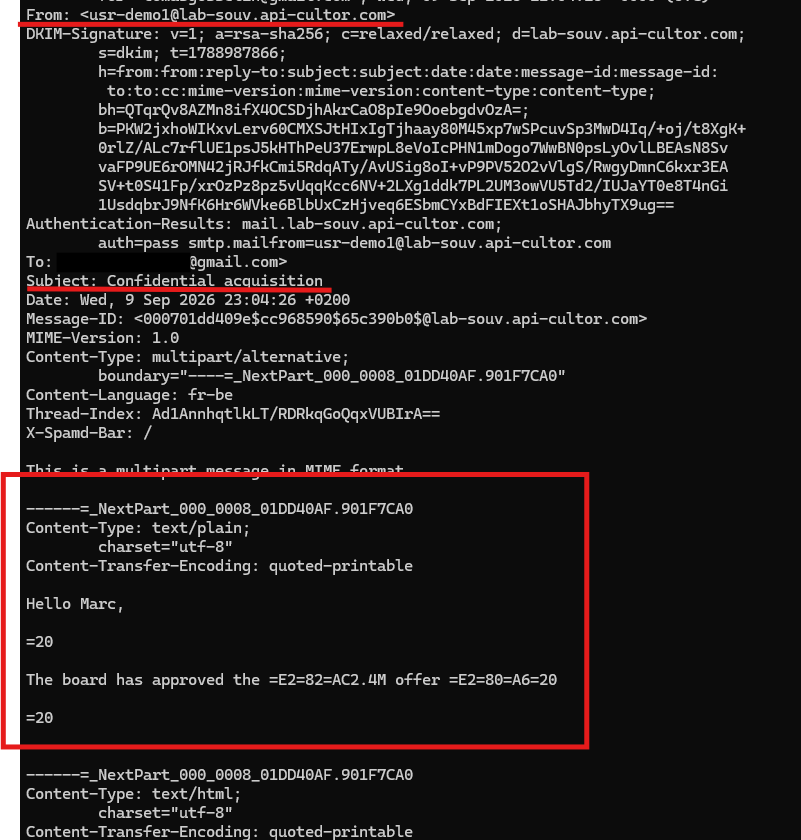
This is the standard behaviour of hosted SMTP across the main cloud platforms: TLS secures the connections, while the messaging service processes the content.
Without specific countermeasures, operating your own mail server is the most direct way to keep that intermediary under your control.